
Cloud Run monitoring keeps an eye on the Google Cloud Run services that host your Google Tag Manager server-side containers. It alerts you on CPU and memory usage, uptime, and SSL certificate expiration, so you know when the server behind your tracking runs into trouble.
This guide walks you through the setup in the Code-Cube.io portal and in Google Cloud Platform (GCP).
What will you do?
- Enable Cloud Run monitoring and enter your GCP project number in the Code-Cube.io portal
- Create a service account with the required roles and upload its key
- Add the Cloud Run services you want to monitor
- Verify that monitoring is active
⏰ Estimated time: 15 - 20 minutes
🔧 Requirements: Access to the Code-Cube.io portal, and access to the GCP project where your GTM server-side Cloud Run services run, with permission to create service accounts and grant roles
- Step 1 – Portal configuration
- 1.1 Enable Cloud Run monitoring
- 1.2 Enter your GCP project number
- Step 2 – Create a GCP service account
- 2.1 Create the service account
- 2.2 Assign the required roles
- 2.3 Generate a service account key
- 2.4 Upload the service account key
- Step 3 – Add your Cloud Run services
- 3.1 Find your Cloud Run details
- 3.2 Add the services in the portal
- 3.3 Start the configuration
- Step 4 – Verify monitoring
- 4.1 Confirm the setup
- 4.2 Resources created in your GCP project
- 4.3 Test monitoring
- Security and privacy
- Next steps
Step 1 – Portal configuration
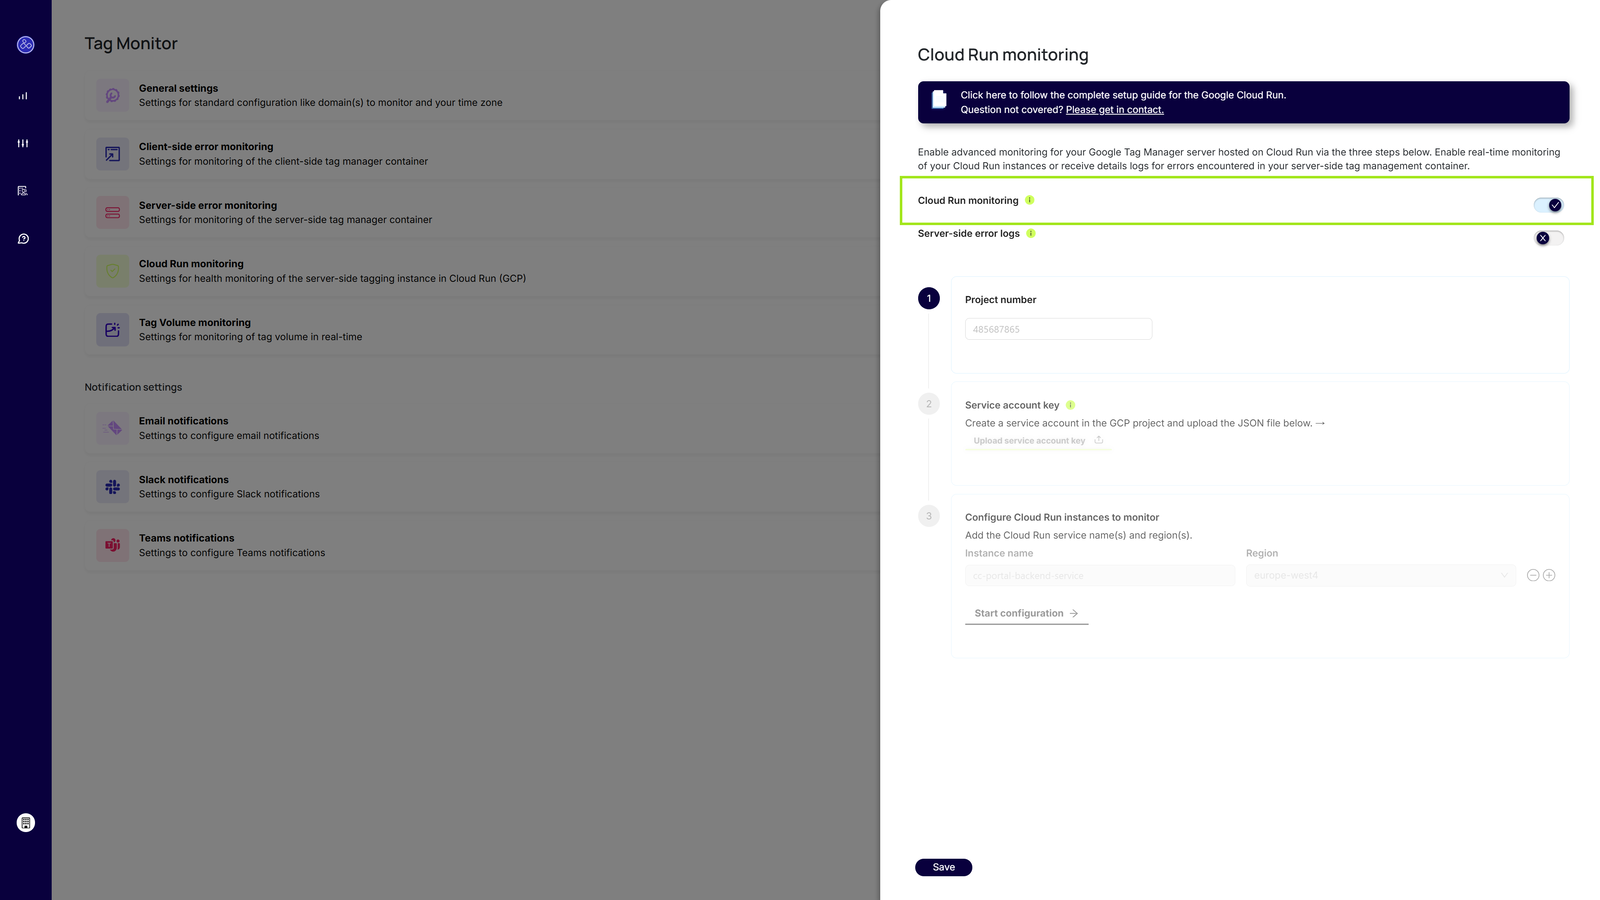
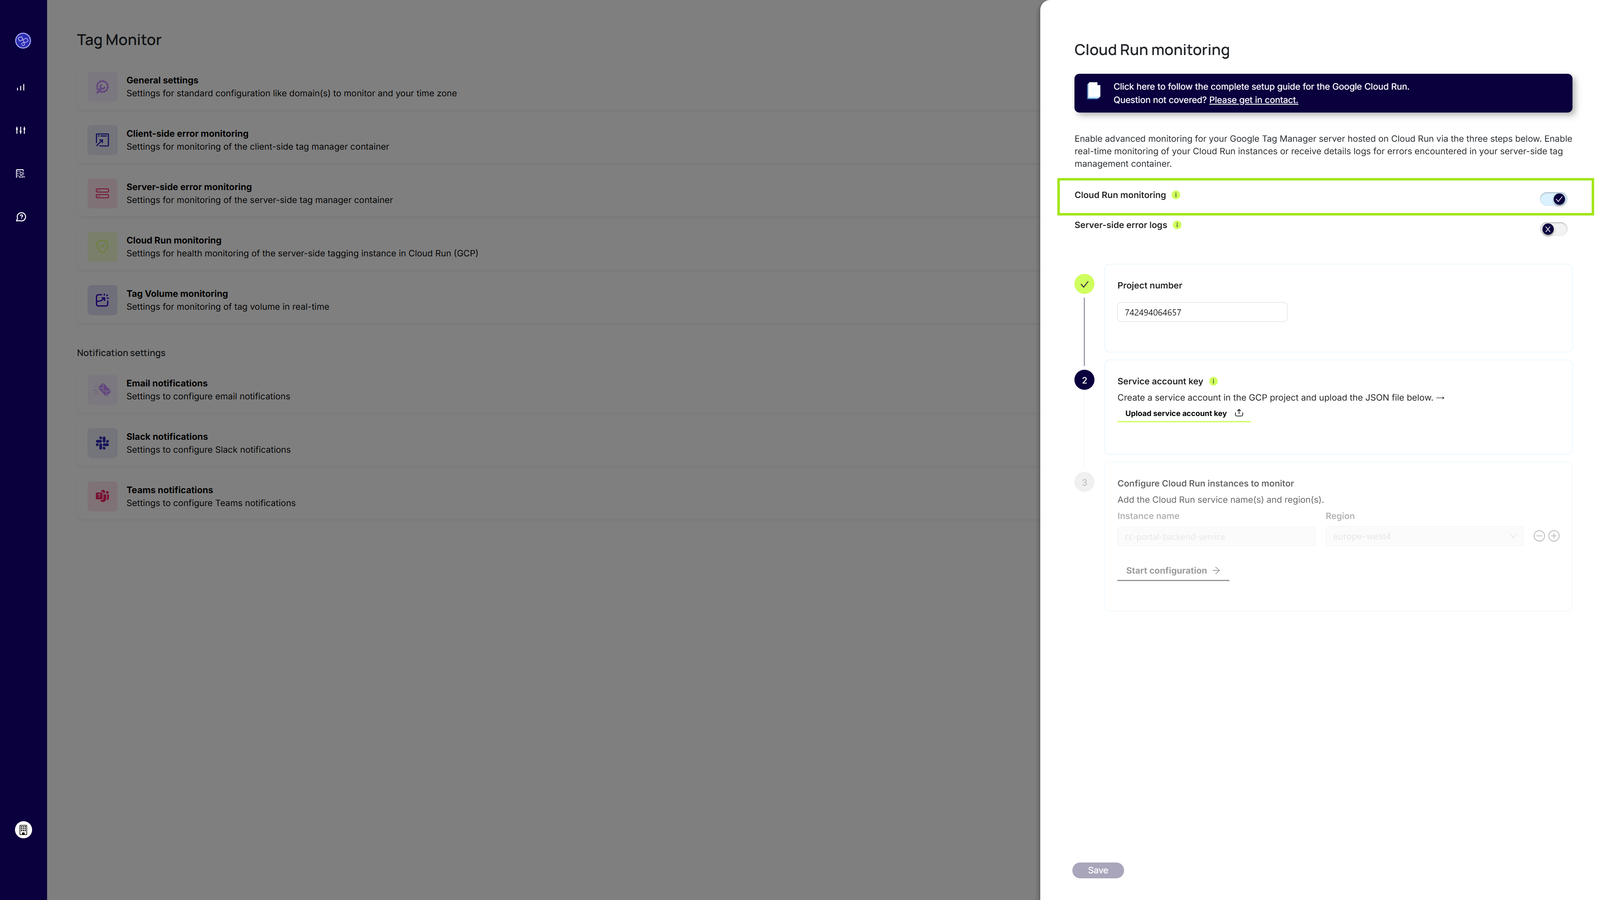
1.1 Enable Cloud Run monitoring
- Go to the Tag Monitor configuration page
- Click the Cloud Run monitoring tab
- Turn on the Cloud Run monitoring toggle
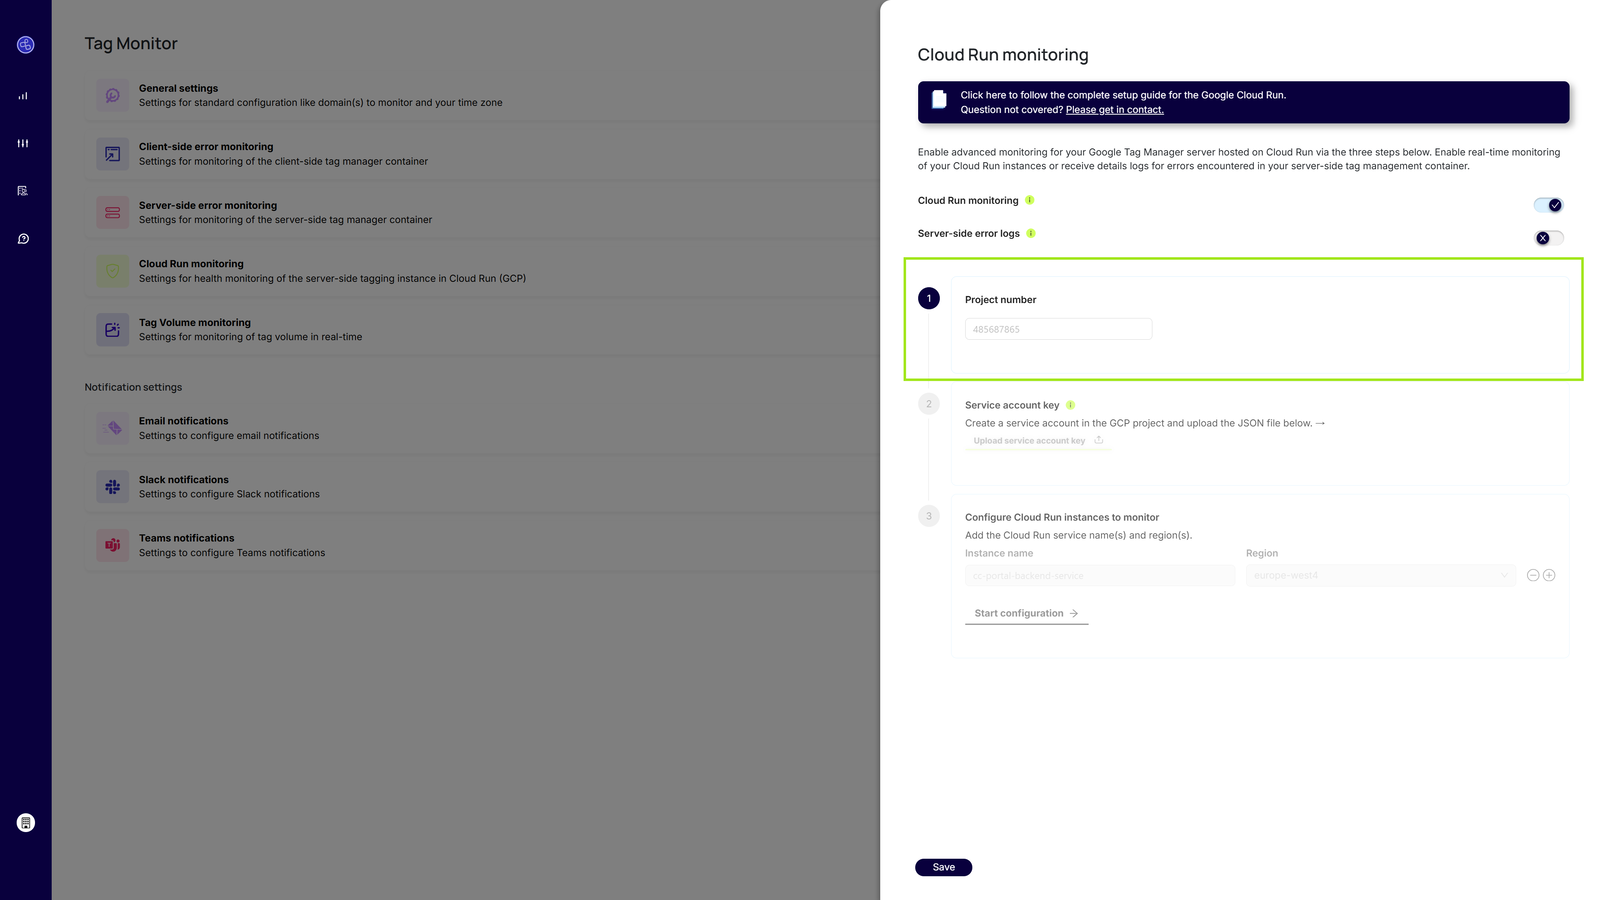
1.2 Enter your GCP project number
Add the GCP project number of the project where your GTM server-side Cloud Run services are deployed.
Important: Monitoring is only available for the GCP project you enter here.
Step 2 – Create a GCP service account
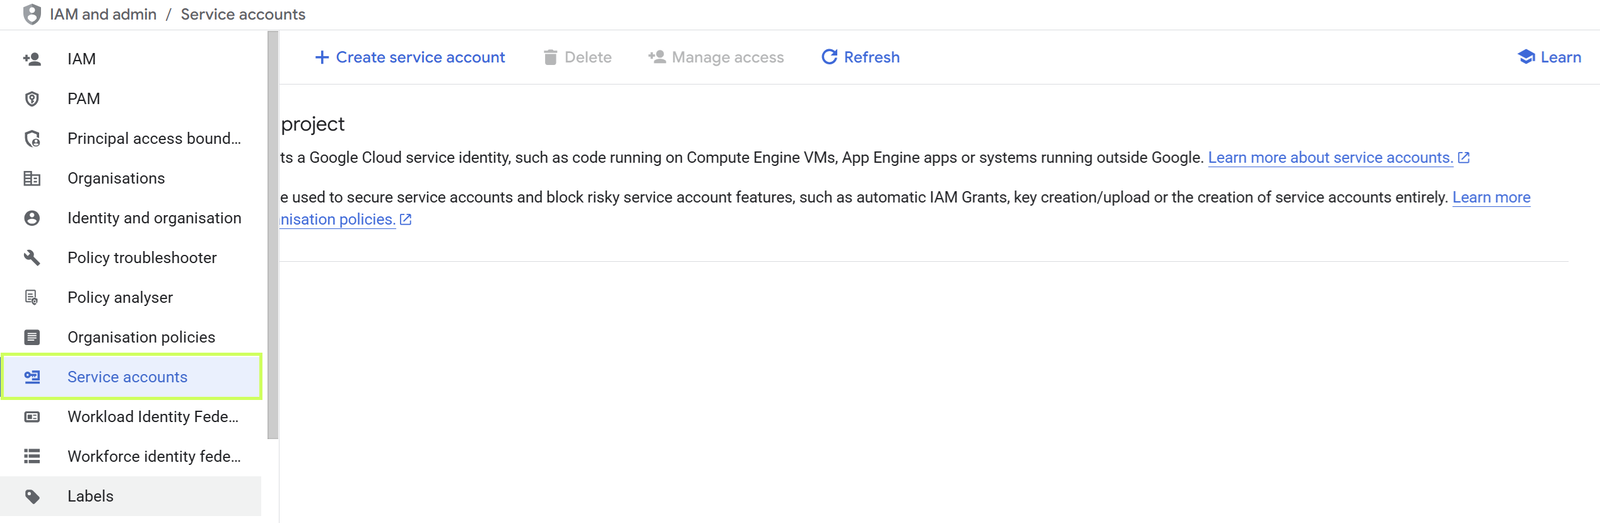
2.1 Create the service account
- In the Google Cloud Console, go to
IAM & Admin>Service Accounts - Click Create service account
- Fill in the details as shown in the screenshot below:
- Service account name and ID: use the same name and ID as in the screenshot
- Service account description: add a description so you can recognize this service account
- Copy the email address shown under Service account ID. You need it in the next step
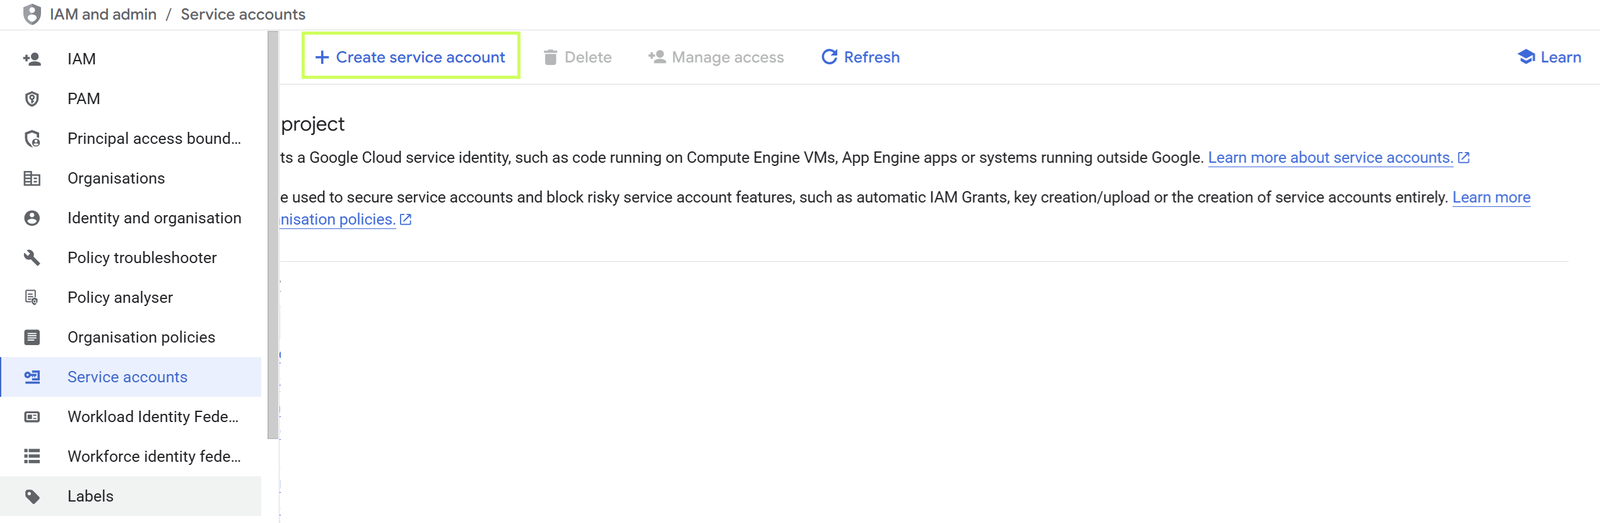
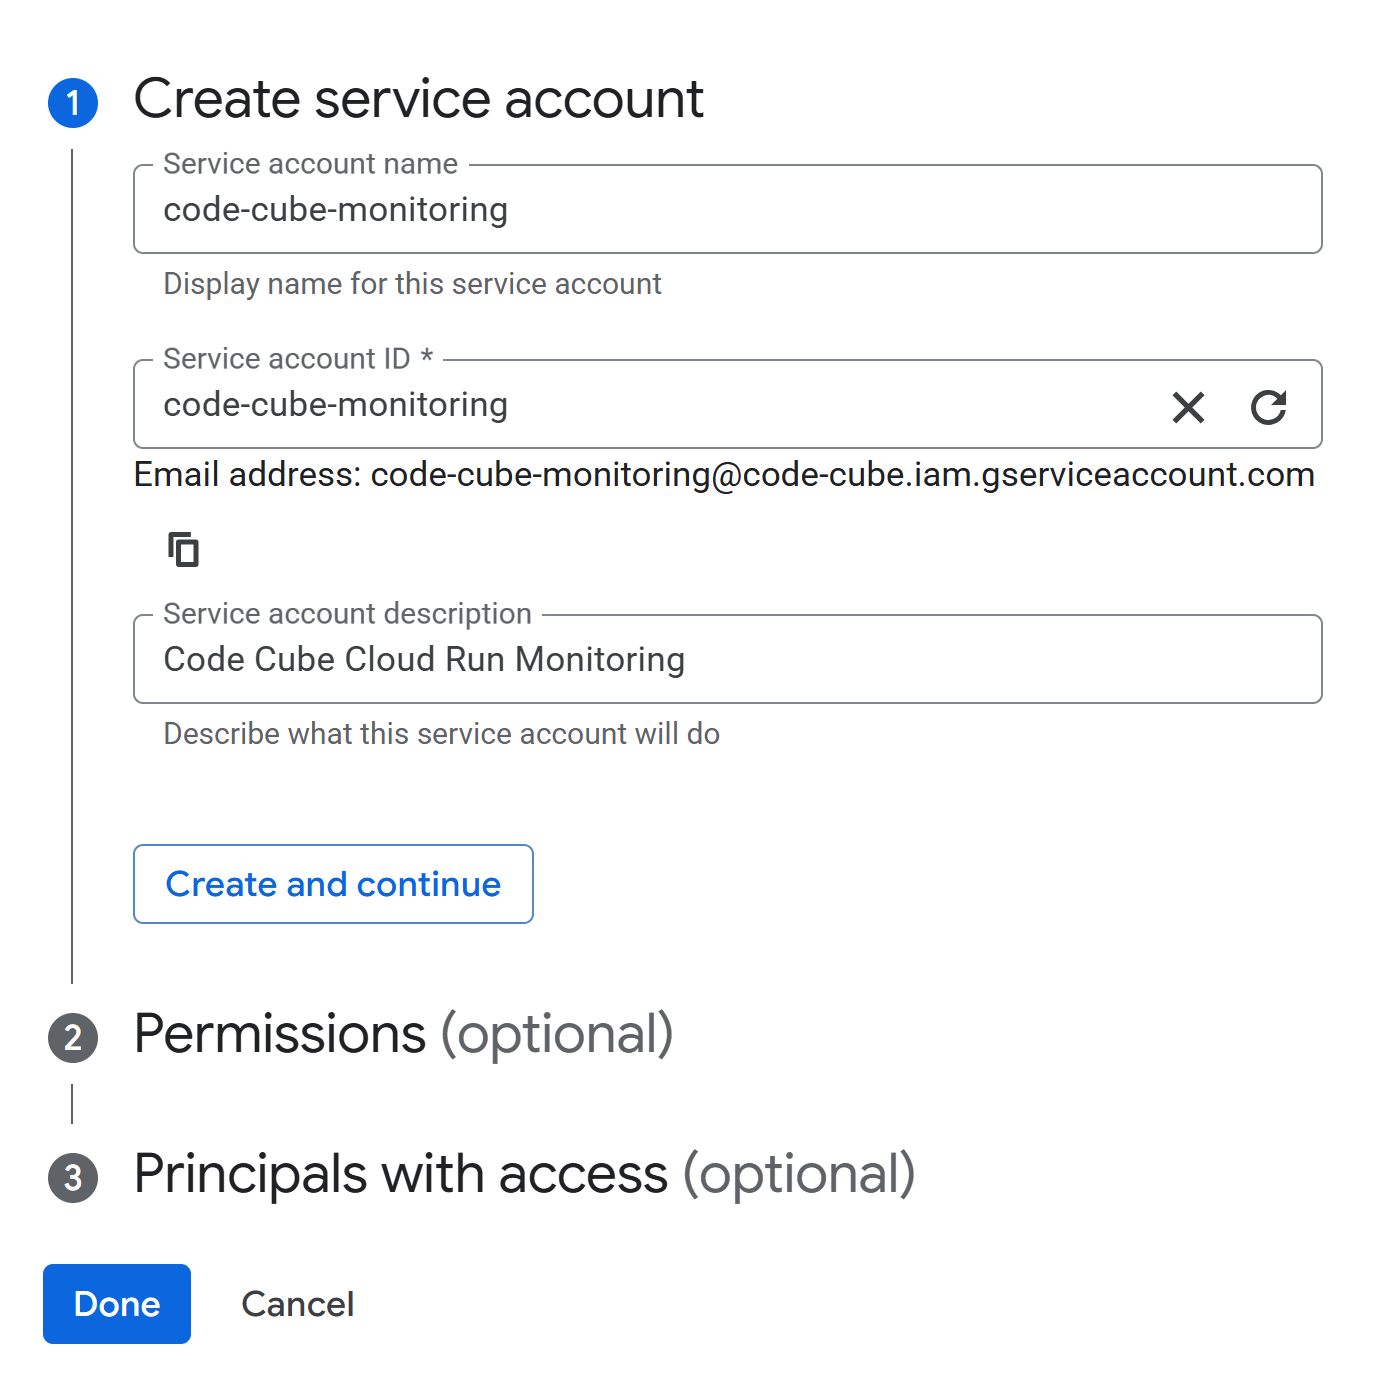
2.2 Assign the required roles
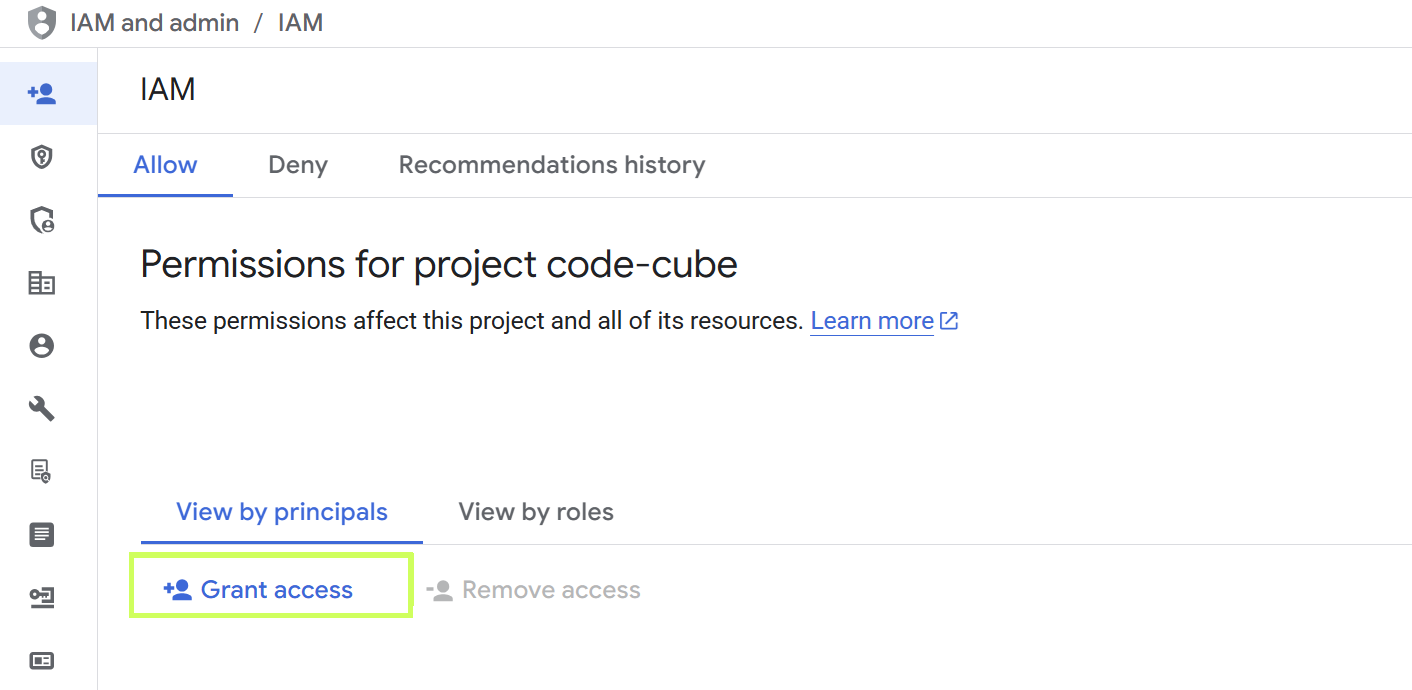
- Go to
IAM & Admin>IAM - Click Grant access
- Paste the service account email into the New principals field
- Assign all roles from the table below
Role | Purpose |
BigQuery Admin | Manages BigQuery datasets used when exporting or analyzing Cloud Run logs and metrics |
Cloud Functions Invoker | Invokes 1st gen HTTP functions with restricted access (2nd gen functions need the Cloud Run Invoker role instead) |
Logging Admin | Manages log-based metrics and alerts for Cloud Run request logs and error events |
Monitoring AlertPolicy Editor | Creates and manages the alert policies that trigger notifications |
Monitoring NotificationChannel Editor (Beta) | Configures and manages the notification channels used by monitoring alerts |
Monitoring Uptime Check Configuration Editor (Beta) | Creates and manages uptime checks for Cloud Run service availability |
Project IAM Admin | Manages the IAM roles and permissions needed to set up and maintain monitoring |
Pub/Sub Admin | Manages the Pub/Sub topics and subscriptions that deliver monitoring alerts |
Pub/Sub Publisher | Publishes monitoring events and alerts to Pub/Sub topics |
Service Account Admin | Creates and manages the service accounts used by monitoring and alerting |
Service Account Token Creator | Generates access tokens for service-to-service authentication |
Service Account User | Lets Cloud Run or monitoring services act as a service account |
Service Usage Admin | Enables and manages the Google Cloud APIs needed for monitoring and logging |
2.3 Generate a service account key
- On the
Service Accountspage, click the three dots next to your service account > Manage keys - Click Add key > Create new key
- Choose JSON and click Create
- The key downloads automatically. Store it securely
2.4 Upload the service account key
- Return to the Code-Cube.io configuration page
- Upload the downloaded JSON key file
- The portal validates the permissions automatically
Security: The service account key is used once during setup and is never stored in Code-Cube.io systems. See Security and privacy below.
Step 3 – Add your Cloud Run services
3.1 Find your Cloud Run details
- In the Google Cloud Console, go to Cloud Run
- Note the service name and region of each GTM server you want to monitor
3.2 Add the services in the portal
For each Cloud Run service, enter:
- Service name: copy from the Cloud Run console
- Region: copy from the Cloud Run console
You can add multiple services.
3.3 Start the configuration
Click Start configuration. Code-Cube.io automatically creates the monitoring resources in your GCP project.
Step 4 – Verify monitoring
4.1 Confirm the setup
- Wait for the Setup successful confirmation message
- Review the list of created monitoring resources
4.2 Resources created in your GCP project
Resource | What it does |
Alert policies | CPU usage, memory usage, uptime checks, and SSL certificate expiration |
Notification channel | Connects the alert policies to a Pub/Sub topic |
Pub/Sub topic and subscription | Handles alert messages and forwards them to a Cloud Function |
Cloud Function | Processes and forwards alert notifications |
Monitoring service account | Named cloud-run-monitoring@{project_id}.iam.gserviceaccount.com, with roles such as Pub/Sub Publisher and Monitoring Admin |
 Notifications & alerts: choose where and how you receive alerts
4.3 Test monitoring
- Check the Code-Cube.io portal dashboard for incoming monitoring data
- Verify that your Cloud Run services appear in the monitoring overview
Security and privacy
Code-Cube.io follows strict security protocols for Cloud Run monitoring:
- One-time use: service account keys are used once during setup and immediately discarded
- Secure processing: all uploads are processed via HTTPS with backend validation
- No credential storage: service account credentials are never stored or cached
- Minimum permissions: only essential GCP resources and permissions are configured
- Dedicated service account: a separate monitoring service account is created with limited scope
For more information, see the Code-Cube.io security documentation.
Still stuck? Contact the Code-Cube.io team.
